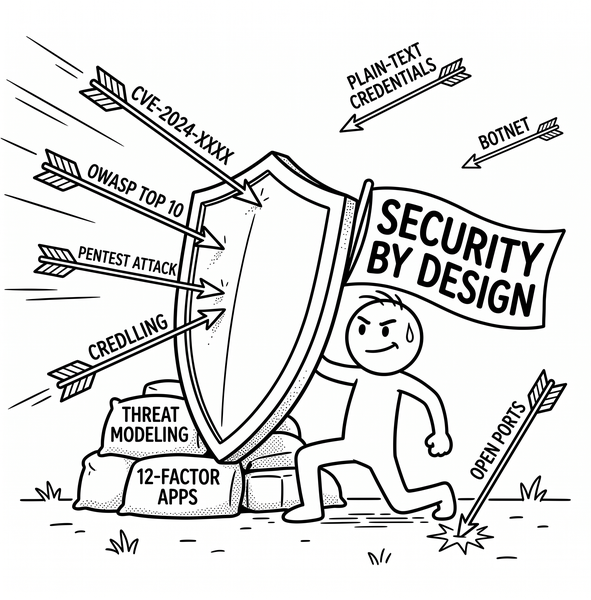
Security by design: stop patching holes you dug yourself
Why security must be integrated from the design phase instead of bolted on at the end: threat modeling, OWASP, 12-Factor Apps, CVEs, and pentesting.
Updated 29 May 2026 · 1 formats
// Same area
Related topics.
Rewriting from scratch: 'hold my beer'
The urge to throw out the code and rewrite from scratch almost always costs more than you think: why we underestimate the real price and when it actually makes sense.
12 min
How to Make Technical Decisions Without Selling Your Soul to the Hype
There are technical decisions, and then there are hype-driven ones. Learn to spot the difference before your team spends the next two years fighting fires in your shiny new architecture.
15 min
Microservices, Monoliths, and Other Mythical Creatures
Monolith or microservices? A calm, noise-free look at both options, real case studies from Netflix, Amazon and Uber, the myths that deserve retirement, and a framework you can actually use to decide.
14 min